Businesses of all sizes in every industry are bombarded with increasing numbers of articles, proposed standards, and advice on what companies should be doing to protect their own informational assets and their customers’ personal data. As the number of data breaches increases, so too does the scrutiny of federal regulators and the plaintiffs’ bar.
In the past several years, not only the FTC and FCC but also the SEC, whose mission is to protect shareholders, have shown growing interest in cybersecurity issues and in ensuring corporations are vigilant in their data management. In the last year, two companies victimized by hackers who stole credit card information have faced high profile civil lawsuits seeking to hold corporate directors and officers liable for damages arising from these crimes. In our hyper-connected, cyber-reliant world, directors, officers and management of all companies must be resilient by educating themselves on both corporate and individual risks related to cybercrime.
Certainly, corporate officers cannot be expected to become corporate IT experts. However, while neither Congress nor the courts have expressly outlined the extent of a director’s duty of care with respect to data security, several recent federal cases offer guidance that both directors and officers could follow in advance of a corporate data-security breach which potentially exposes sensitive information of third parties that the company possesses.


The Takeaway: Disc-o Fever
Staff Reports
-
Oct 2, 2026
|
|
Investors Buy Leland Apartments In Nearly $58M Deal
Staff Reports
-
Oct 2, 2026
|
|
Big Projects Having Or Set To Have Major Local Impacts
Emma Dill
-
Oct 2, 2026
|
|
Comfort Food In Burgaw
Beth A. Klahre
-
Oct 2, 2026
|
|
Trends To Watch: Economic Development
Emma Dill
-
Oct 2, 2026
|
|
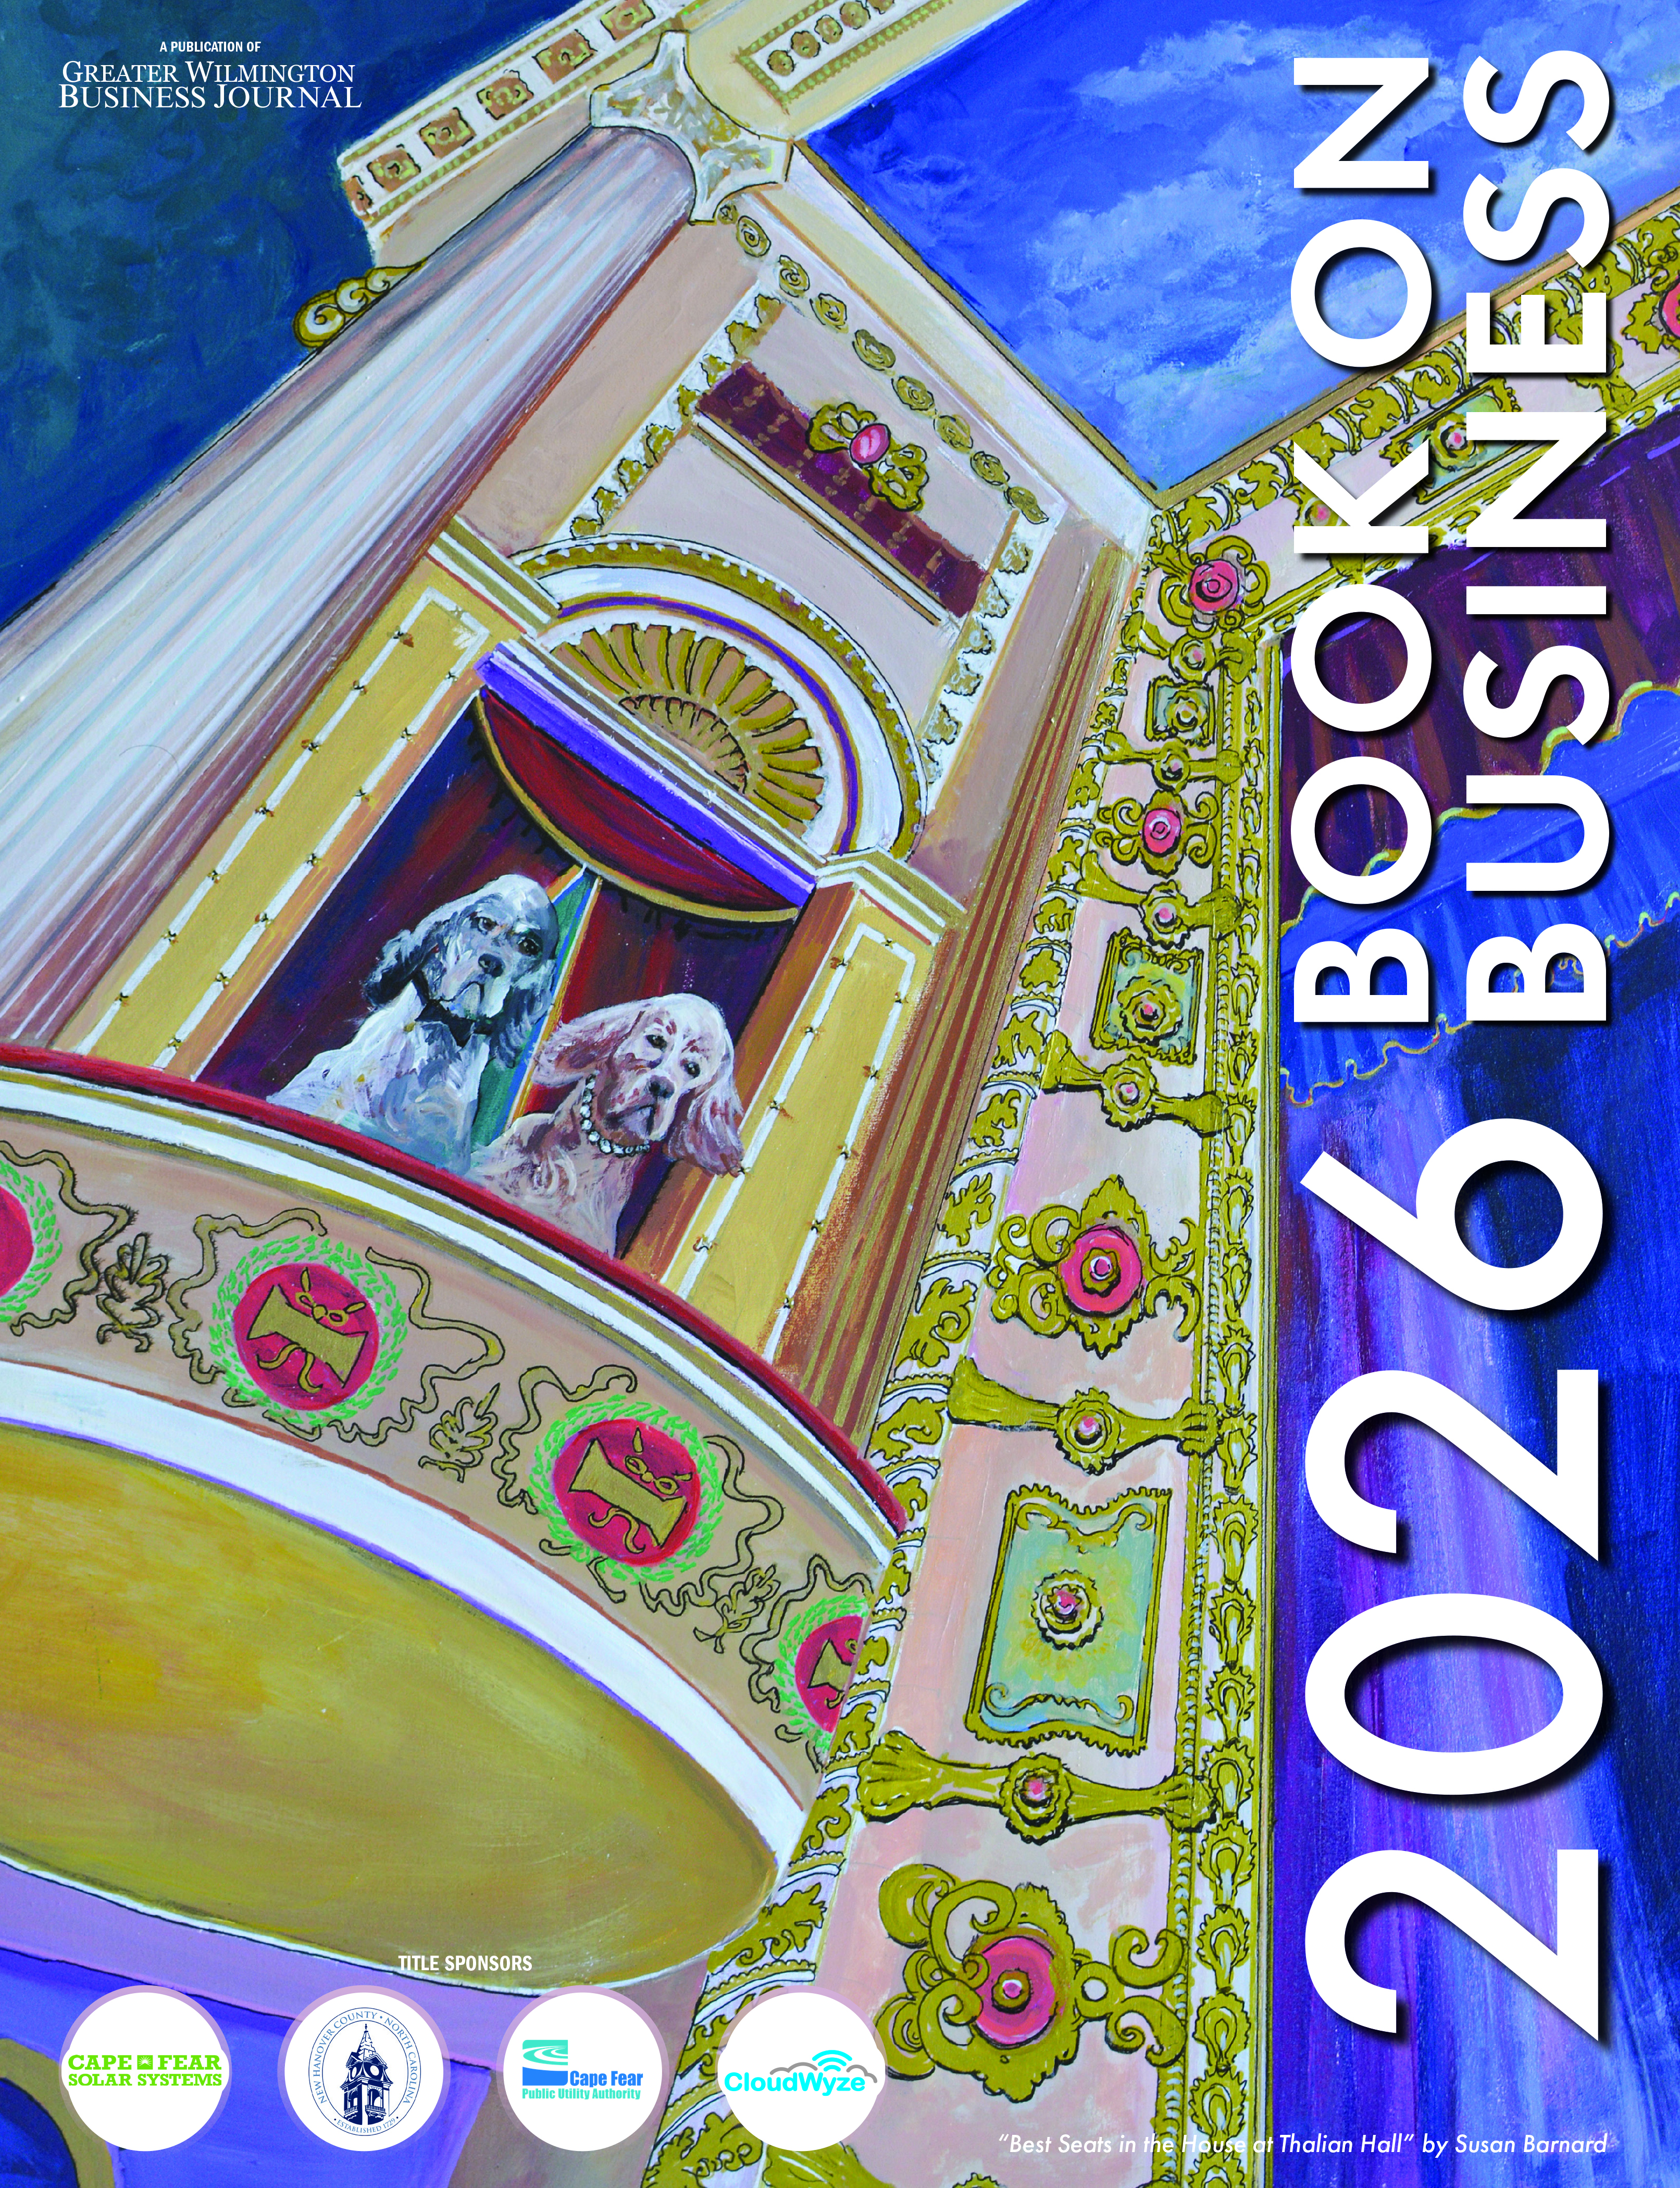
The 2026 WilmingtonBiz: Book on Business is an annual publication showcasing the Wilmington region as a center of business.